The digital age has fundamentally transformed how we navigate our daily lives, streamlining everything from global commerce and communication to personal finance and entertainment. However, this unprecedented level of convenience has introduced a parallel rise in sophisticated cyber threats. In the early days of the internet, users operated largely on blind faith, assuming that the websites they visited were inherently safe. Today, that paradigm has shifted entirely. Trust can no longer be assumed; it must be actively verified. The anatomy of digital trust is now built on verifiable technical standards, rigorous cybersecurity frameworks, and strict regulatory oversight. Whether you are buying a product from an overseas e-commerce vendor or submitting sensitive documents to a financial portal, recognizing the anatomy of a secure platform is the ultimate prerequisite for online safety.
Just as you would rigorously verify an online bank’s credentials, physical address, and regulatory compliance before depositing your hard-earned money, you must apply the exact same level of scrutiny to any digital platform handling your sensitive data. This principle is arguably most critical in the iGaming and online casino industry, a sector where massive volumes of financial transactions and personal information are exchanged continuously. For instance, successfully identifying a legális online kaszinó relies entirely on checking these universal markers of digital trust and safety. A legally operating and secure platform in the entertainment or financial sector doesn’t just promise security; it proves it through a visible, verifiable, and standardized digital architecture that protects the consumer at every touchpoint.
The Foundation of Data Transit: SSL and TLS Encryption
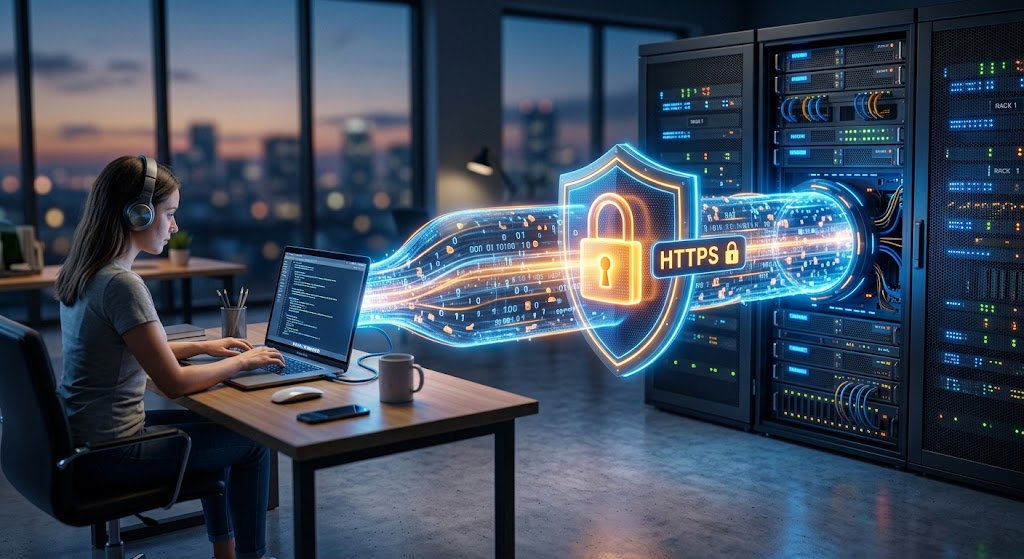
At the very core of digital trust is the secure transmission of data. Whenever you interact with a website, information is constantly transmitted between your internet browser and the site’s hosting server. Without adequate protection, this transit phase is highly vulnerable to interception by malicious actors — a scenario commonly known as a “man-in-the-middle” attack. This is where Transport Layer Security (TLS), the modern and significantly more secure successor to Secure Sockets Layer (SSL), becomes absolutely indispensable.
TLS is a complex cryptographic protocol that provides end-to-end communication security over a computer network. When a platform employs robust TLS encryption, any data traveling between your device and the server — be it your login credentials, credit card numbers, or personal identification details — is immediately scrambled into an unreadable ciphertext. Even if a cybercriminal manages to intercept the data packet while it is in transit, it remains entirely useless without the specific, highly complex decryption key held exclusively by the receiving server.
For the everyday internet user, this complex cryptographic handshake is represented by simple, universally recognized trust signals: the “HTTPS” prefix in the website’s URL and the small padlock icon positioned in the browser’s address bar. While these indicators were once considered premium features reserved only for banks and high-tier e-commerce giants, they are now the absolute baseline for web security. Leading global security authorities strictly outline guidelines for configuring these protocols to ensure maximum data confidentiality. If a platform does not feature an active, verifiable SSL/TLS certificate, it immediately fails the most fundamental test of digital trust and should be avoided entirely.
System Integrity and Defensive Architecture
While encrypted data transit is vital, it only protects information while it is moving. The anatomy of trust requires that the platform itself — the software architecture where your data ultimately resides — is fortified against internal breaches, unauthorized access, and malicious code injections. A secure platform is built upon a philosophy of “security by design,” meaning that defensive protocols are baked into the software’s source code from the very beginning, rather than applied as a reactive afterthought.
To achieve this high level of systemic integrity, reputable digital platforms align their development and operational practices with globally recognized cybersecurity frameworks. One of the most prominent benchmarks in the tech industry is the OWASP Top 10. Curated by the Open Worldwide Application Security Project, this standard identifies the most critical and prevalent security risks facing web applications today. These risks include vulnerabilities such as broken access control, cryptographic failures, and harmful data injection flaws.
A platform that genuinely prioritizes user safety will continuously test its infrastructure against these exact vulnerabilities. This involves deploying automated threat detection tools, enforcing strict multi-factor authentication (MFA) protocols for account access, and regularly subjecting their systems to independent penetration testing — often referred to as ethical hacking. By actively simulating cyberattacks based on established frameworks, platforms can identify and patch microscopic vulnerabilities before they can be exploited by real-world threat actors. For users, recognizing that a platform actively invests in these invisible, backend security measures is a profound indicator of institutional trustworthiness.
The Intersection of Digital Licensing and Regulatory Compliance
Technical infrastructure, no matter how sophisticated, represents only one half of the trust equation. The other half is governed by operational legitimacy, legal accountability, and regulatory compliance. A platform might utilize state-of-the-art encryption, but if the corporate entity operating it is not legally bound to protect consumer rights, the user remains at significant risk. Therefore, strict regulatory licensing acts as the ultimate guarantor of digital trust.
In heavily scrutinized sectors such as decentralized finance, e-commerce, and particularly iGaming, obtaining a legitimate operating license is a grueling, resource-intensive process. Regulatory authorities require platforms to undergo exhaustive audits that scrutinize everything from their corporate financial health and data privacy policies to the fairness of their operational algorithms. Furthermore, global security standards — such as the ISO/IEC 27001 — mandate that organizations establish, implement, and continually improve a comprehensive Information Security Management System (ISMS). This ensures that a company’s approach to securing data is not just an ad-hoc effort, but a structurally embedded business practice.
Daniel Orosz, iGaming expert and senior author at TopKaszinok.com, emphasizes how deeply intertwined technical security and legal compliance have become in the modern digital landscape. He notes, “Technical encryption means very little if the corporate entity holding your data isn’t legally bound to protect it. Today, true platform legitimacy requires a seamless integration of high-level cybersecurity protocols with uncompromising regulatory compliance. A verified license isn’t just a piece of digital paper; it is a legally binding promise that the platform operates under strict oversight, ensuring genuine consumer protection and fair play.”
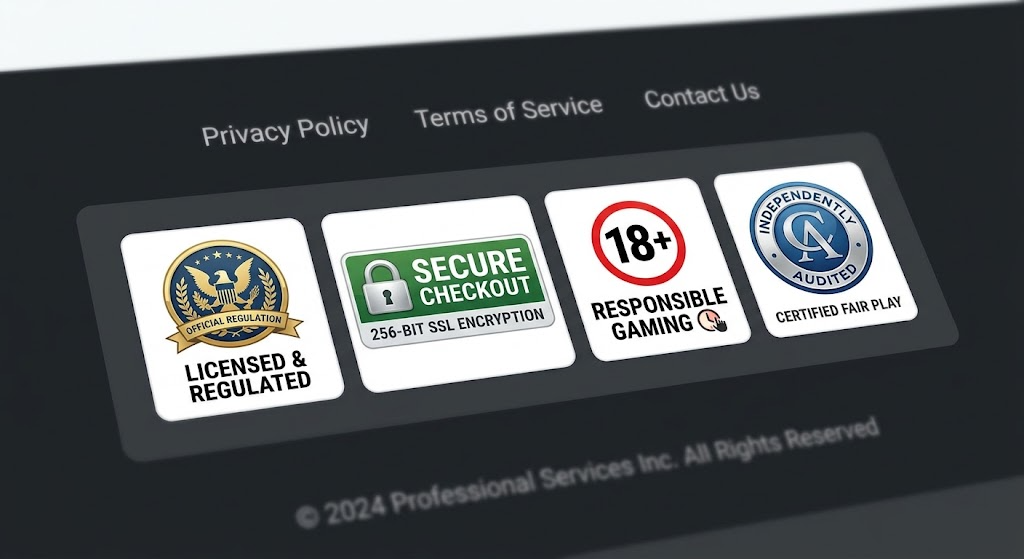
This intersection of tech and law is exactly why regulatory badges, license numbers, and certifications from independent testing agencies are prominently displayed on secure websites. They serve as verifiable proof that the platform has opened its technical and operational doors to strict government and independent scrutiny.
Empowering the User: Proactive Trust Verification
Understanding the anatomy of trust empowers consumers to navigate the internet proactively rather than reactively. Recognizing secure platforms is not an innate skill; it requires a systematic, disciplined approach to verifying a website’s credentials before committing any personal data or financial resources.
First, users should habitually check for standard cryptographic indicators, such as valid HTTPS connections and up-to-date SSL/TLS certificates. Secondly, they must look for transparent privacy policies that clearly dictate how user data is collected, stored, and utilized. If a platform’s privacy policy is obfuscated, overly complex, or non-existent, it should be treated as a major red flag.
Finally, users must actively seek out and verify regulatory licensing and independent audit seals. These are typically located in the footer of a website’s homepage. However, simply seeing a logo is not enough; secure platforms will hyperlink these trust badges directly to the official regulatory body’s database, allowing the user to confirm the license’s active status and validity in real-time.
Conclusion
The concept of trust in the digital age is far removed from the blind optimism of the early internet. Today, trust is a highly structured, measurable, and verifiable concept. By understanding the critical importance of secure data transit through TLS encryption, the necessity of rigorous software integrity tested against global frameworks, and the non-negotiable requirement of strict regulatory licensing, users can confidently separate legitimate platforms from high-risk entities. Ultimately, whether you are engaging in e-commerce, managing digital assets, or participating in online entertainment, your safety relies on your ability to recognize these foundational pillars of digital security. In an era of escalating cyber threats, an educated and vigilant user will always be the most effective firewall.